
Download Remote Control for Mac & Classic Apple TV iPhone and iPod Touch
Download link
Torrent Mirror

Available link for download

 --

 CVE-2013-1563
Oracle Java 7 Update 17, and possibly other versions, allows remote attackers to execute arbitrary code via unspecified vectors, as demonstrated by Ben Murphy during a Pwn2Own competition at CanSecWest 2013.CVE-2013-2418 - Unspecified details.

Available link for download

Available link for download
Available link for download

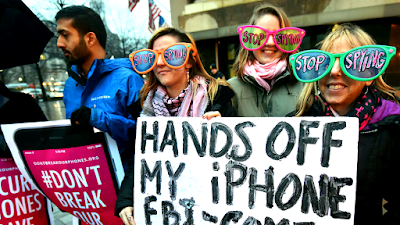
A few hours ago, the US Department of Justice filed to vacate tomorrows hearing, as it has apparently found another method to access the San Bernardino shooters work-owned iPhone 5c. The filing says that on Sunday, an "outside party demonstrated to the FBI a possible method for unlocking Farooks iPhone" which "should eliminate the need for the assistance from Apple Inc. ("Apple") set forth in the All Writs Act Order in this case." . . .DOJ Motion To Vacate Hearing
The government is planning to perform more testing on the iPhone 5c to determine suitability of the proposed procedure, and report back to the courts on April 5 with progress, which may yet result in Apple having to appear and defend its position.

Available link for download

About Java for Mac OS X 10.6 Update 13
Java for Mac OS X 10.6 Update 13 delivers improved security, reliability, and compatibility by updating Java SE 6 to 1.6.0_41.
On systems that have not already installed Java for Mac OS X 10.6 update 9 or later, this update will configure web browsers to not automatically run Java applets. Java applets may be re-enabled by clicking the region labeled "Inactive plug-in" on a web page. If no applets have been run for an extended period of time, the Java web plug-in will deactivate.
Please quit any web browsers and Java applications before installing this update.
About the security content of Java for OS X 2013-002 and Mac OS X v10.6 Update 14
Impact: Multiple vulnerabilities in Java 1.6.0_41
Description: Multiple vulnerabilities existed in Java 1.6.0_41, the most serious of which may allow an untrusted Java applet to execute arbitrary code outside the Java sandbox. Visiting a web page containing a maliciously crafted untrusted Java applet may lead to arbitrary code execution with the privileges of the current user. These issues were addressed by updating to Java version 1.6.0_43. Further information is available via the Java website at
http://www.oracle.com/technetwork/java/javase/releasenotes-136954.html
CVE-ID
CVE-2013-0809
CVE-2013-1493
About Java for OS X 2013-002
Java for OS X 2013-001 delivers improved security, reliability, and compatibility by updating Java SE 6 to 1.6.0_41.
On systems that have not already installed Java for OS X 2012-006, this update disables the Java SE 6 applet plug-in. To use applets on a web page, click on the region labeled "Missing plug-in" to download the latest version of the Java applet plug-in from Oracle.
Please quit any web browsers and Java applications before installing this update.
About the security content of Java for OS X 2013-002 and Mac OS X v10.6 Update 14
Impact: Multiple vulnerabilities in Java 1.6.0_41
Description: Multiple vulnerabilities existed in Java 1.6.0_41, the most serious of which may allow an untrusted Java applet to execute arbitrary code outside the Java sandbox. Visiting a web page containing a maliciously crafted untrusted Java applet may lead to arbitrary code execution with the privileges of the current user. These issues were addressed by updating to Java version 1.6.0_43. Further information is available via the Java website at
http://www.oracle.com/technetwork/java/javase/releasenotes-136954.html
CVE-ID
CVE-2013-0809
CVE-2013-1493
Java software for your computer, or the Java Runtime Environment, is also referred to as the Java Runtime, Runtime Environment, Runtime, JRE, Java Virtual Machine, Virtual Machine, Java VM, JVM, VM, or Java download.
Oracle Security Alert for CVE-2013-1493
Description
This Security Alert addresses security issues CVE-2013-1493 (US-CERT VU#688246) and another vulnerability affecting Java running in web browsers. These vulnerabilities are not applicable to Java running on servers, standalone Java desktop applications or embedded Java applications. They also do not affect Oracle server-based software.
These vulnerabilities may be remotely exploitable without authentication, i.e., they may be exploited over a network without the need for a username and password. For an exploit to be successful, an unsuspecting user running an affected release in a browser must visit a malicious web page that leverages these vulnerabilities. Successful exploits can impact the availability, integrity, and confidentiality of the users system.
Due to the severity of these vulnerabilities, and the reported exploitation of CVE-2013-1493 "in the wild," Oracle strongly recommends that customers apply the updates provided by this Security Alert as soon as possible.

Available link for download


Available link for download